
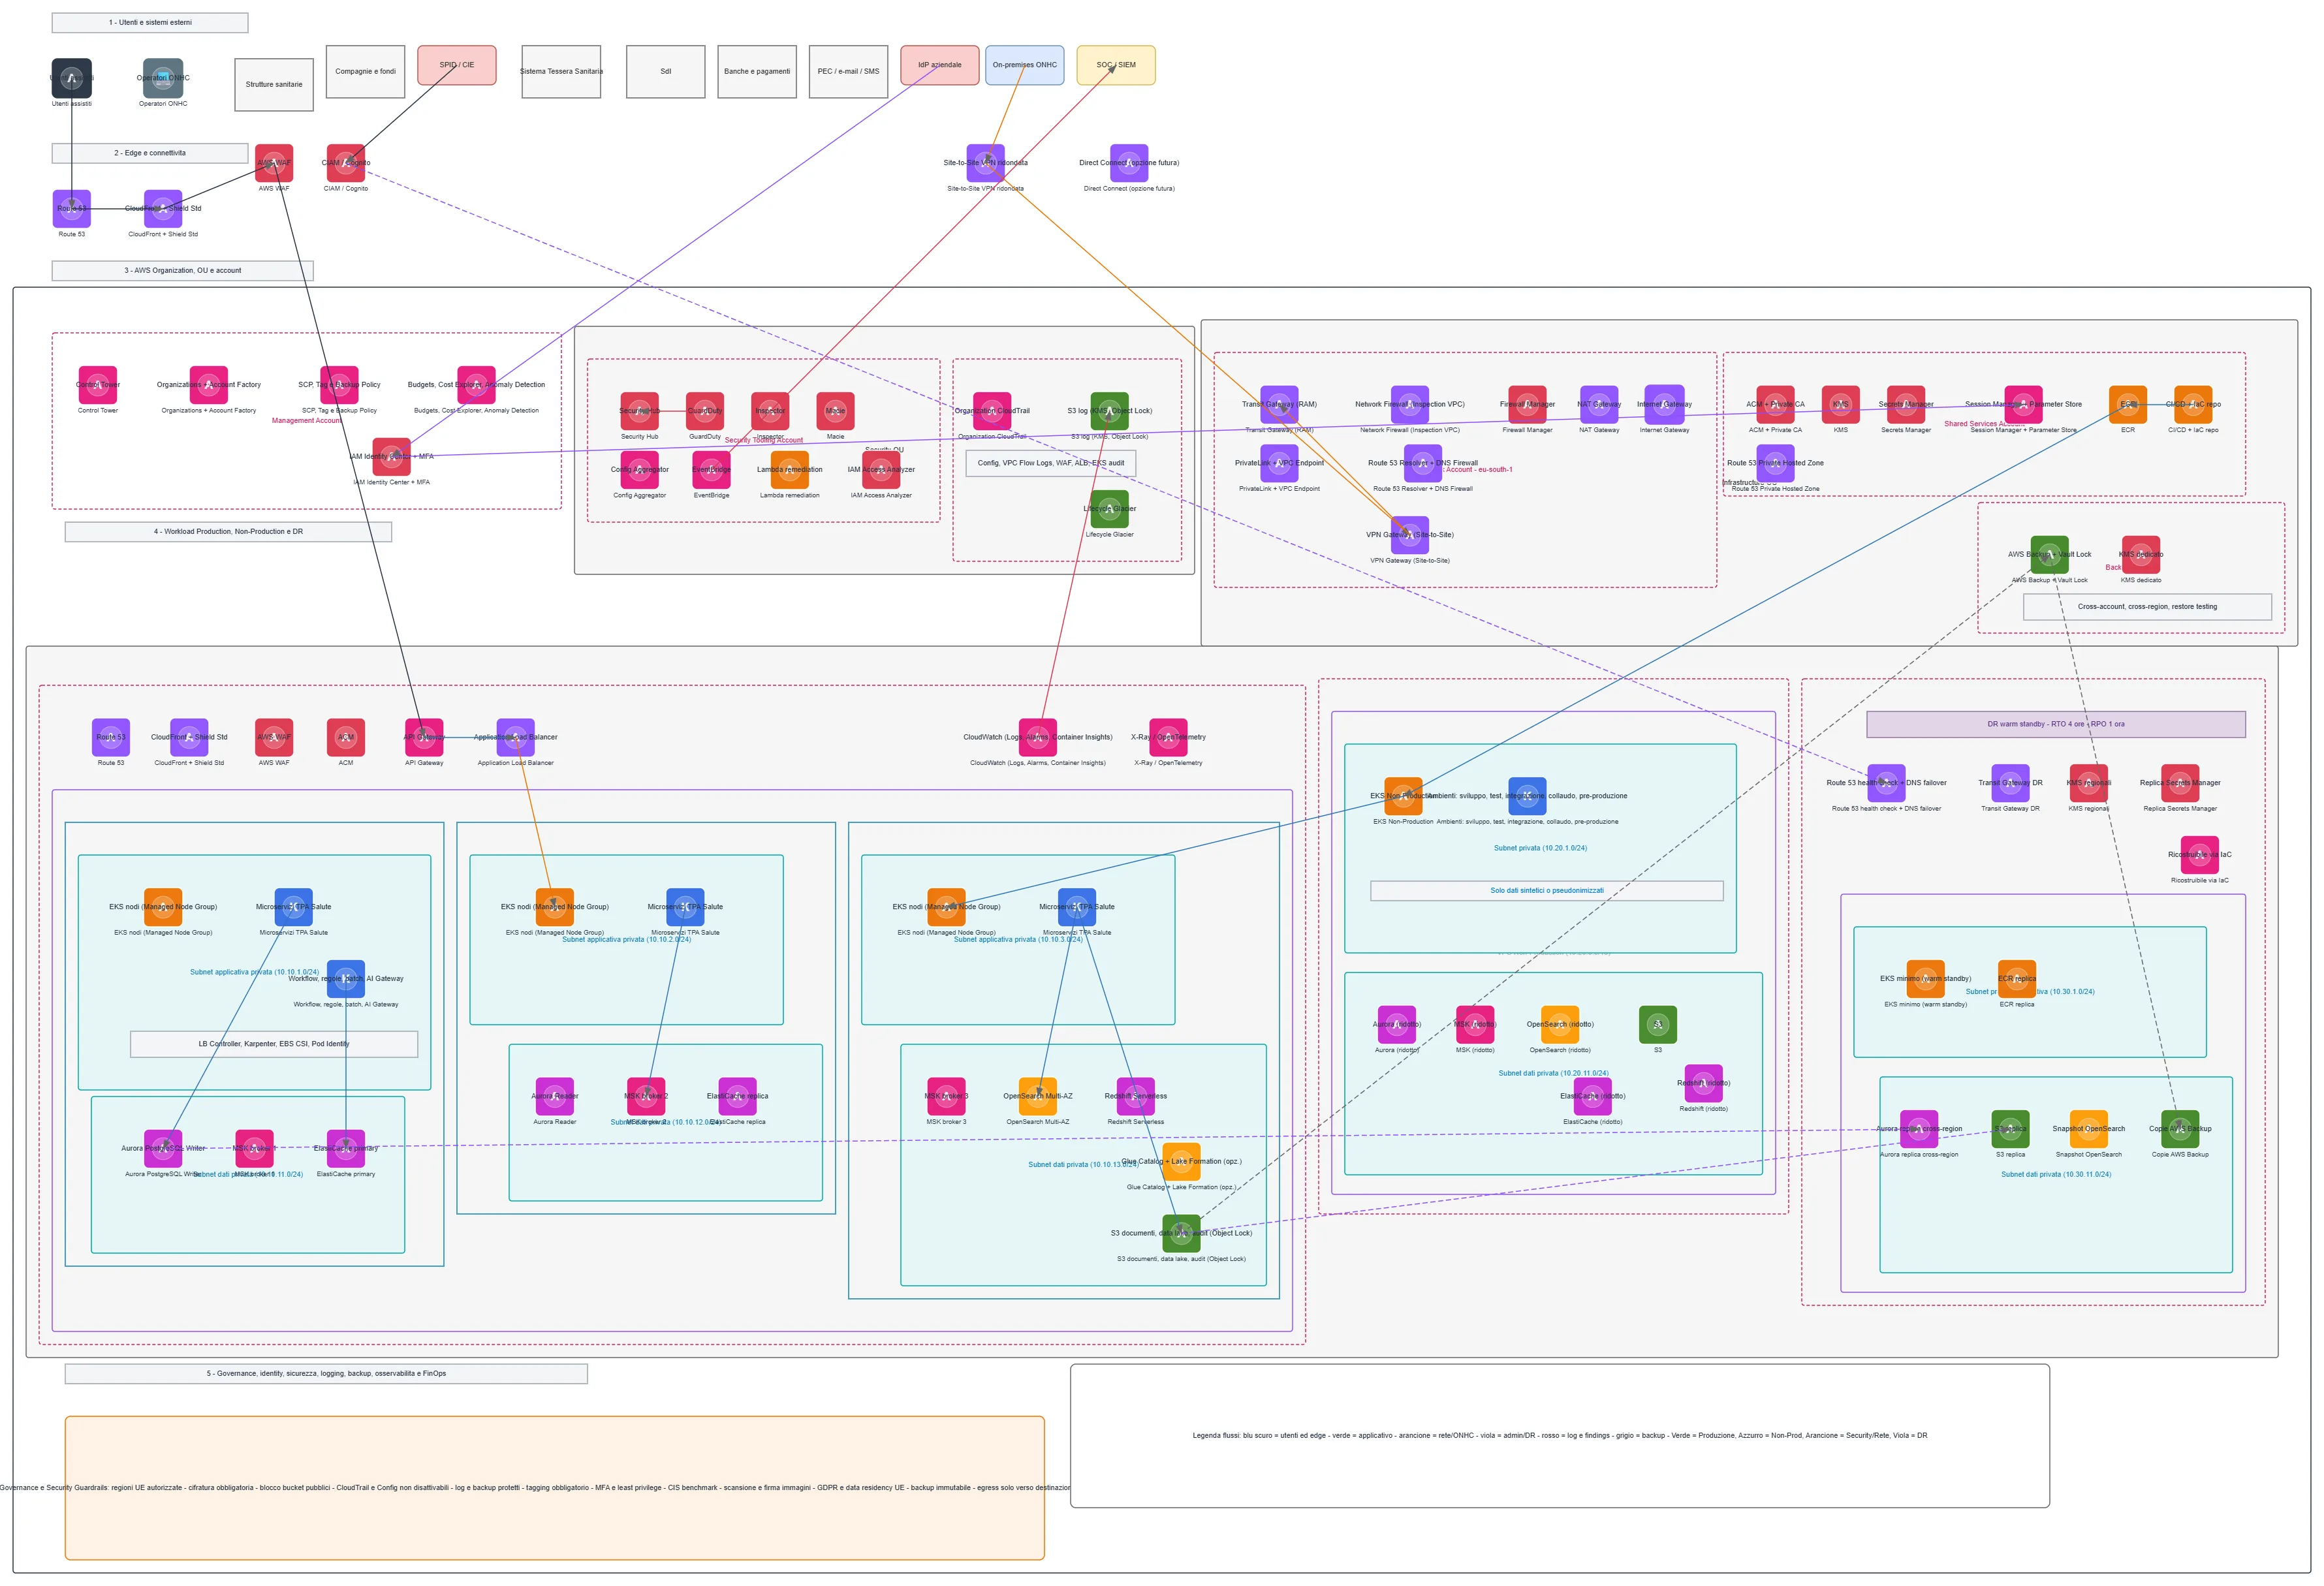
About This Architecture
AWS multi-account landing zone architecture for TPA Salute healthcare platform integrating SPID/CIE authentication, on-premises connectivity via Site-to-Site VPN, and centralized security governance through AWS Control Tower. Network flows from external users and healthcare providers through Route 53, CloudFront with AWS WAF, and Cognito CIAM into isolated workload accounts spanning three availability zones in eu-south-1. Production workloads run containerized microservices on EKS with Aurora PostgreSQL, MSK, ElastiCache, and OpenSearch, while centralized accounts handle security (GuardDuty, Security Hub, Inspector), logging (S3 with Object Lock), and backup orchestration. This architecture demonstrates defense-in-depth for GDPR/Italian healthcare compliance, with Network Firewall inspection, cross-account IAM Identity Center, and automated remediation via EventBridge and Lambda. Fork this diagram on Diagrams.so to customize account structure, add regions, or integrate additional AWS services like AppConfig or Systems Manager for your healthcare workloads.