
About This Architecture
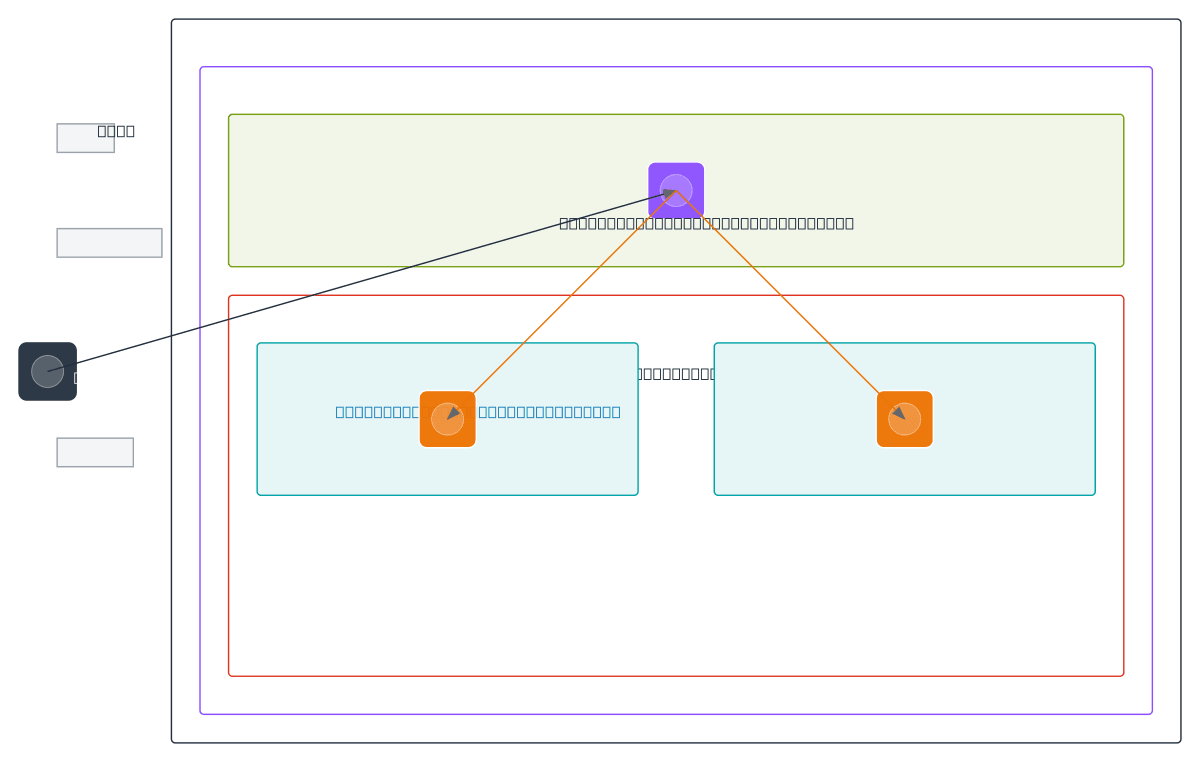
Internal Application Load Balancer distributing traffic across EC2 instances in private subnets within a VPC. Users connect to the ALB in the public subnet, which routes requests to t3.medium EC2 instances deployed across Private Subnet A and Private Subnet B using the 10.0.0.0/16 CIDR block. This architecture isolates application servers from direct internet exposure while maintaining high availability through multi-AZ deployment and load balancing. Fork this diagram on Diagrams.so to customize security groups, add NAT gateways, or extend with RDS backends. Consider adding a Network ACL layer for defense-in-depth if your compliance requirements demand additional network segmentation.